Information Security Management
Robust lifecycle controls across OMNISOFT, ensuring strict data handling protocols for all decentralized digital ecosystems.
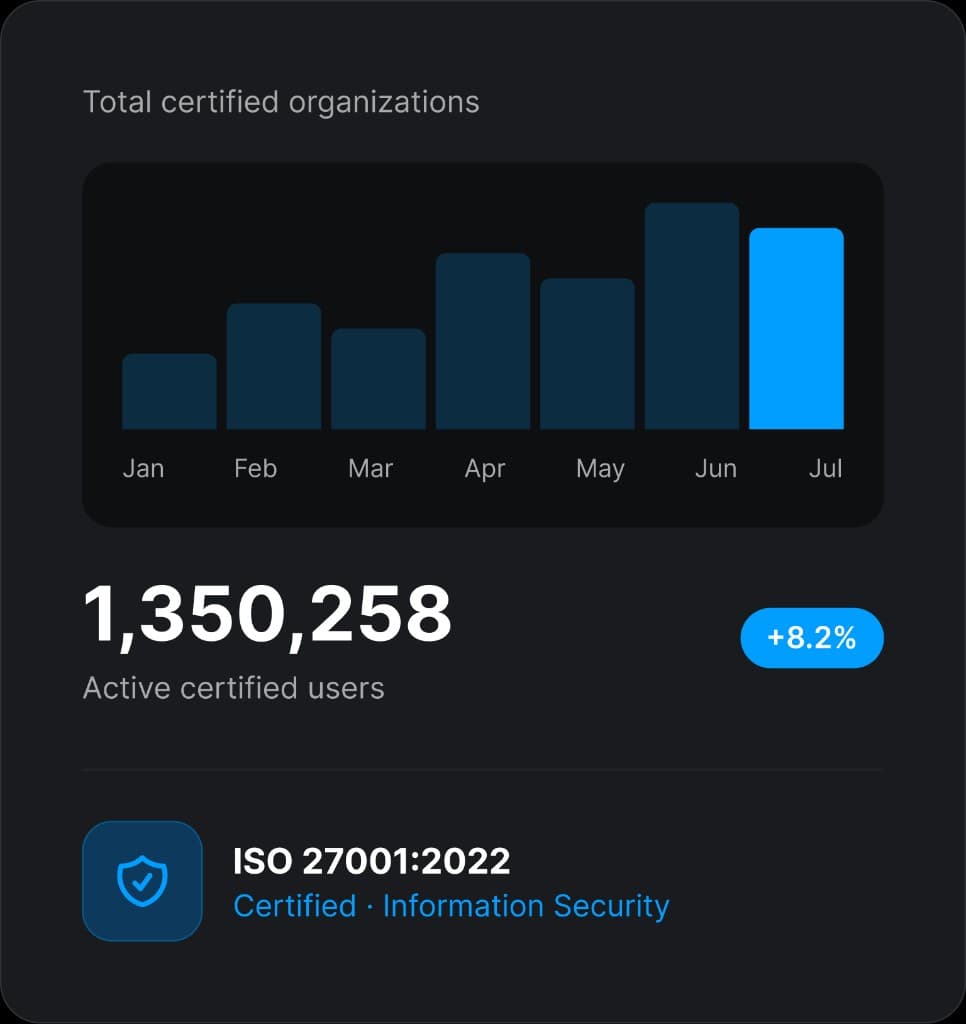
OMNISOFT places data protection and risk management at the core of all operations. Our comprehensive information security management system (ISMS) is certified to meet global enterprise standards, safeguarding your web3 platforms and cloud systems.
Core Principles
Our verified ISO framework ensures that every line of smart contract code, cloud network run, and API layer is protected against advanced threat landscapes.
Robust lifecycle controls across OMNISOFT, ensuring strict data handling protocols for all decentralized digital ecosystems.
Continuous identification, analysis, and mitigating actions of software vulnerabilities and structural platform risks.
Isolated build pipelines, secure code repositories, verified dependencies, and multi-tier signature checking.
Compliance with modern data residency regulations, secure key storage protocols, and state-of-the-art encryption algorithms.
System Safeguards
Our ISMS architecture covers the full spectrum of modern cloud security, decentralized smart contracts, and corporate engineering habits.
Access Security
Strict Role-Based Access Controls (RBAC) paired with verified Multi-Factor Authentication (MFA) across all administration levels.
Threat Response
24/7/365 proactive monitoring with pre-defined playbook protocols. Real-time alert triggers flag unexpected transaction structures instantly.
Operational Integrity
Every cloud provider, code library, and technology tool under OMNISOFT operations undergoes continuous third-party risk analysis.
Lifecycle Audits
We run regular external penetration testing, internal team compliance courses, and complete security posture reviews monthly.
Our Roadmap
Every software engineering client receives full compliance integration, matching our rigorous ISO internal checklist to your operational requirements.
Step 01
Analyze client requirements, map transaction flows, and set rigorous security parameters prior to writing code.
Step 02
Implement verified cryptographic modules, strict credential storage, and air-gapped system isolation rules.
Step 03
Develop with real-time static code analysis and run simulated vulnerability exploits inside test environments.
Step 04
Platform launch backed by continuous logging, automatic cloud-health signals, and active database integrity monitoring.
Client Benefits
Developing with an ISO 27001 certified agency transfers instant security credibility to your investors, users, and business partners.
Drastically shorten your internal IT compliance review times. Our pre-vetted pathways make institutional due-diligence simple.
All platforms utilize zero-knowledge principles and strictly partitioned databases to enforce strict enterprise privacy boundaries.
Launch knowing your systems are built specifically to satisfy complex digital asset, web3, and cross-border regulatory frameworks.
FAQ
Frequently asked questions about our ISO 27001:2022 certification standard and what it means for your platforms.
ISO 27001:2022 is the gold standard for global information security management systems. It mandates continuous verification of risk controls, physical and digital safeguards, and continuous auditing—guaranteeing your web3 or cloud code remains highly secure.
Yes. Because our internal secure-coding pipelines, dependency checks, and operations comply with certified standards, the foundations of the software we build for you instantly pass enterprise security audits easily.
Our information security management system is reviewed through monthly internal audits, paired with comprehensive annual surveillance assessments completed by certified independent external registrars.
We structure decentralized products so that sovereign client keys, user data, and analytical payloads reside in encrypted environments matching strict international data residency regulations.
Build secure blockchain products, smart contracts, dApps, and decentralized platforms with Omnisoft.
Join the Omnisoft newsletter for Web3 insights, blockchain trends, smart contract updates, and product launch tips.
Our team will respond to you within the next 12-16 hours with the support you need.
Send Message